Website privacy: cookies, tracking and clear choices
Which services does your website load, when is consent needed and does the implementation match the information provided?
A cookie banner can look reassuring while optional services are already running in the background. The useful first question is therefore practical: what does this website load before a visitor has made a choice?
This article explains a technical review process for German business websites. It provides general information and does not replace individual legal advice.
Two questions: device access and personal data
Section 25 of Germany’s TDDDG concerns storing information on a device or accessing information already stored there. Consent is generally required. The two exceptions concern transmission of a communication and access that is strictly necessary to provide a digital service expressly requested by the user. These are narrow conditions, not a blanket exemption for everything a website operator finds useful. Source: Section 25 TDDDG.
Processing personal data is a separate question under the GDPR. A service can require assessment even without cookies. Conversely, a necessary session cookie does not mean every subsequent use of the resulting data is permitted.
Start with an inventory, not a banner purchase
Open the website in a fresh browser profile and record its requests and storage entries. Include the homepage, forms, maps, videos and pages containing third-party widgets. For each service, note its purpose, provider, data, loading trigger and retention period. Ask which function visitors actually need.
A website without consent-dependent processing may not need a consent banner. Necessary functionality and privacy information still require attention. Whether a particular tool needs consent depends on its configuration and operation, not just its product name. The Hessian data protection authority’s cookie FAQ explains this distinction.
Make accepting and rejecting clear
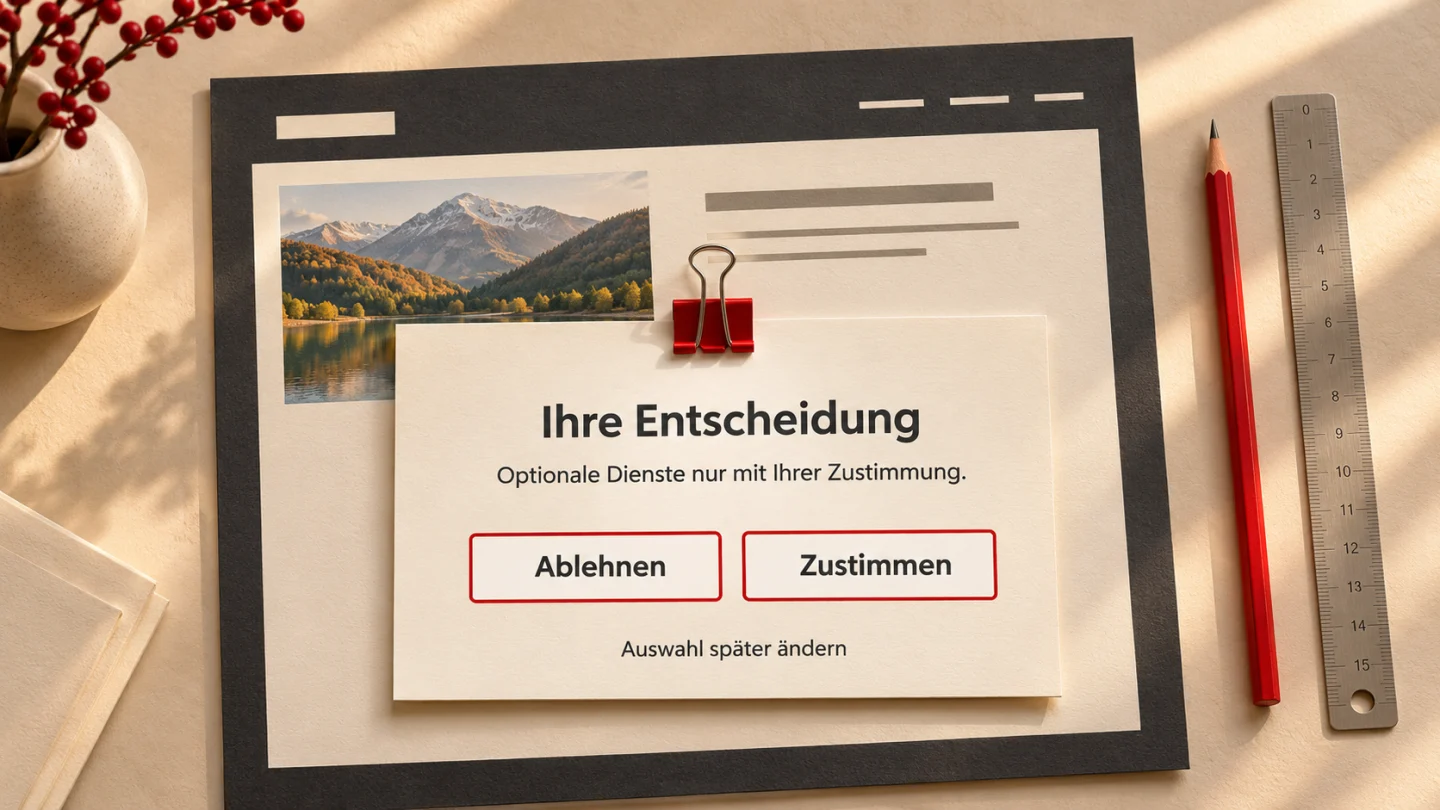
If a banner offers an accept-all option, provide a clearly visible reject-all option on the first layer. Do not bury refusal behind additional settings. The Lower Saxony supervisory authority describes the relevant 2025 court decision.
Optional choices should start off. Explain the purposes and provide an accessible way to withdraw consent. The EDPB assesses misleading colours and contrast case by case: there is no universal pixel specification that certifies a banner. Source: EDPB Cookie Banner Taskforce.
For implementation, use two clearly labelled actions with comparable visual weight. Check them on a narrow phone display, with a keyboard and at increased text size. A prominent button that disappears below the fold is not a convincing choice.
Reduce unnecessary external connections
- Fonts: where licensing permits, serve font files yourself. This removes that external font request.
- Maps and videos: consider a normal link or an informative placeholder. If consent is required, the embedded service must not load before it is given.
- Analytics: define the question you want to answer before installing another tool. “Cookieless” does not automatically mean anonymous or exempt from consent.
- Chat and newsletter tools: assess them separately. A newsletter subscription and a support conversation have different purposes and data flows.
These are design options to evaluate, not automatic compliance certificates. Self-hosting, an EU server location or a vendor’s consent feature alone does not settle every legal question.
Test four states, not just the first visit
- Before choosing: check what is requested and stored without interaction.
- After rejecting: reload and navigate to another page. Optional tracking should remain blocked.
- After accepting: check that only the selected categories are activated.
- After withdrawing: verify that future consent-dependent activity stops. Review storage handling and the next visit as well.
Keep a short test record with the date, pages, choices and observed requests. Repeat the checks after changing analytics, embeds or the consent setup. A scanner can help find entries, but does not explain their purpose or legal basis.
Privacy information must match the implementation
Explain who processes personal data, why, on what basis, for how long and who receives it. Include applicable rights, complaint information and relevant transfers. Collect only what the purpose needs. Review provider roles and obtain processing agreements where the arrangement requires them. The European Commission’s GDPR guidance provides the underlying principles.
Assign responsibility for keeping this information current. A new booking widget can change the data flow even when the rest of the website looks identical. Technical checks and qualified legal review should use the same service inventory.
A manageable next step
List the services, remove those without a useful purpose and align the remaining integrations with the consent choices. Then test the complete journey. This produces a clearer website and a concrete basis for reviewing privacy questions.